
Docker in Production: A Deployment Checklist Beyond the Dockerfile
Prepare Docker applications for production with better images, safe configuration, health checks, logging and persistent-data plans.
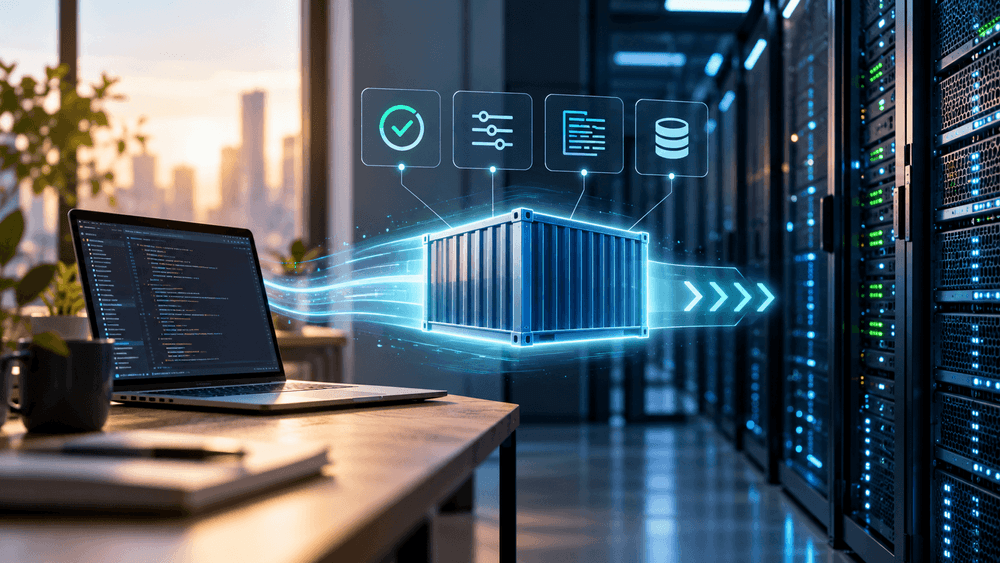
A Dockerfile makes it possible to package an application, but it does not make the application ready for production. The image must be trustworthy, the service must receive configuration safely, and operators must know what happens when a process starts, stops or fails.
These questions matter whether the container runs on one server, a managed application platform or Kubernetes. Solve them at the application boundary before expecting orchestration to compensate for them.
Build an Image You Can Explain and Rebuild
Choose a maintained base image from a source you trust. Use a multi-stage build when the compiler and development tools are not needed at runtime. Docker's build best practices recommend keeping the runtime image focused and rebuilding images as dependencies and base images change.
Record the source commit and image version. A mutable tag such as latest is convenient during development, but it is a poor record of what production actually runs. Pin or record the image digest for deployments where exact reproducibility matters. Scan the image, review findings in context and define who owns updates to the base image and application dependencies.
For example, a .NET or Node.js API may compile and test in one stage, then copy only the runtime output into a smaller final image. The image should still be tested as the image that will be deployed; a successful test of source code alone does not prove its runtime configuration works.
Keep Configuration and Secrets Outside the Image
The same application image should be usable in staging and production with different environment configuration. Do not bake database passwords, API tokens or production URLs into image layers. Use the hosting platform's secret mechanism and restrict which services and people can read each value.
Check what the application logs. A correctly stored secret can still leak if a startup error prints its connection string or a debug endpoint exposes the environment. Configuration changes should be reviewable and reversible just like code changes.
Make Start, Stop and Failure Behavior Predictable
The container needs a clear main process, a way to report readiness and a graceful shutdown path. Readiness means the service can handle requests, not merely that its process exists. During an update, give active requests time to finish before the old instance disappears. On Kubernetes, these behaviors connect to probes and rollout settings; our production-ready Kubernetes checklist covers the platform side.
Set sensible resource requests or limits for the hosting environment and observe real usage before tuning them. A memory limit that is too low can create repeated restarts; an oversized request can waste capacity or prevent scheduling. Test the application under the load and dependency failures it may meet in production.
Decide Where Logs and Data Live
Containers are replaceable. Application logs should go to a collection path that survives replacement, and persistent data needs storage and backups designed for its consistency requirements. A database running in a container still needs database-aware backup and recovery; packaging it does not create a recovery plan.
Make a simple inventory: which files must persist, where logs are collected, which external services are required and what the application does when one of them is unavailable. This inventory also helps decide whether a single-server deployment is sufficient or whether the team needs an orchestration platform. Our guide to when to use Kubernetes provides that decision framework.
Use a Production Readiness Review
Before the first live deployment, ask an engineer who did not write the Dockerfile to build the image, find the version, run it with non-production secrets, stop it cleanly and trace its logs. Then rehearse a failed update and recovery. The resulting fixes are usually more valuable than adding another tool to the stack.
Check the boundary with the host
The host or platform still supplies networking, storage, process scheduling and the path for image updates. Decide who patches the host OS, who updates the container runtime and who notices when available disk space is running low. If the application depends on a database outside the host, test its connection and failure behavior from the deployed environment, not only from a developer laptop.
A production review should also check what happens after a restart. Does the application start in the correct order, receive its secrets and reconnect safely? Can two copies run at once during a rollout, or does the application assume exclusive access to a local file? These details determine whether the service can scale and update without surprising users.
If your team needs help turning an application image into a dependable service, Codativity can review the image, deployment path and operating requirements together.
20/11/2026
Contact Us
701, Opal Tower Business Bay, Dubai United Arab Emirates
P.O.Box 126732

Let's Work Together
© 2016 - 2026 Codativity Software Solutions. All Rights Reserved.